DTS Identity
DTS Identity
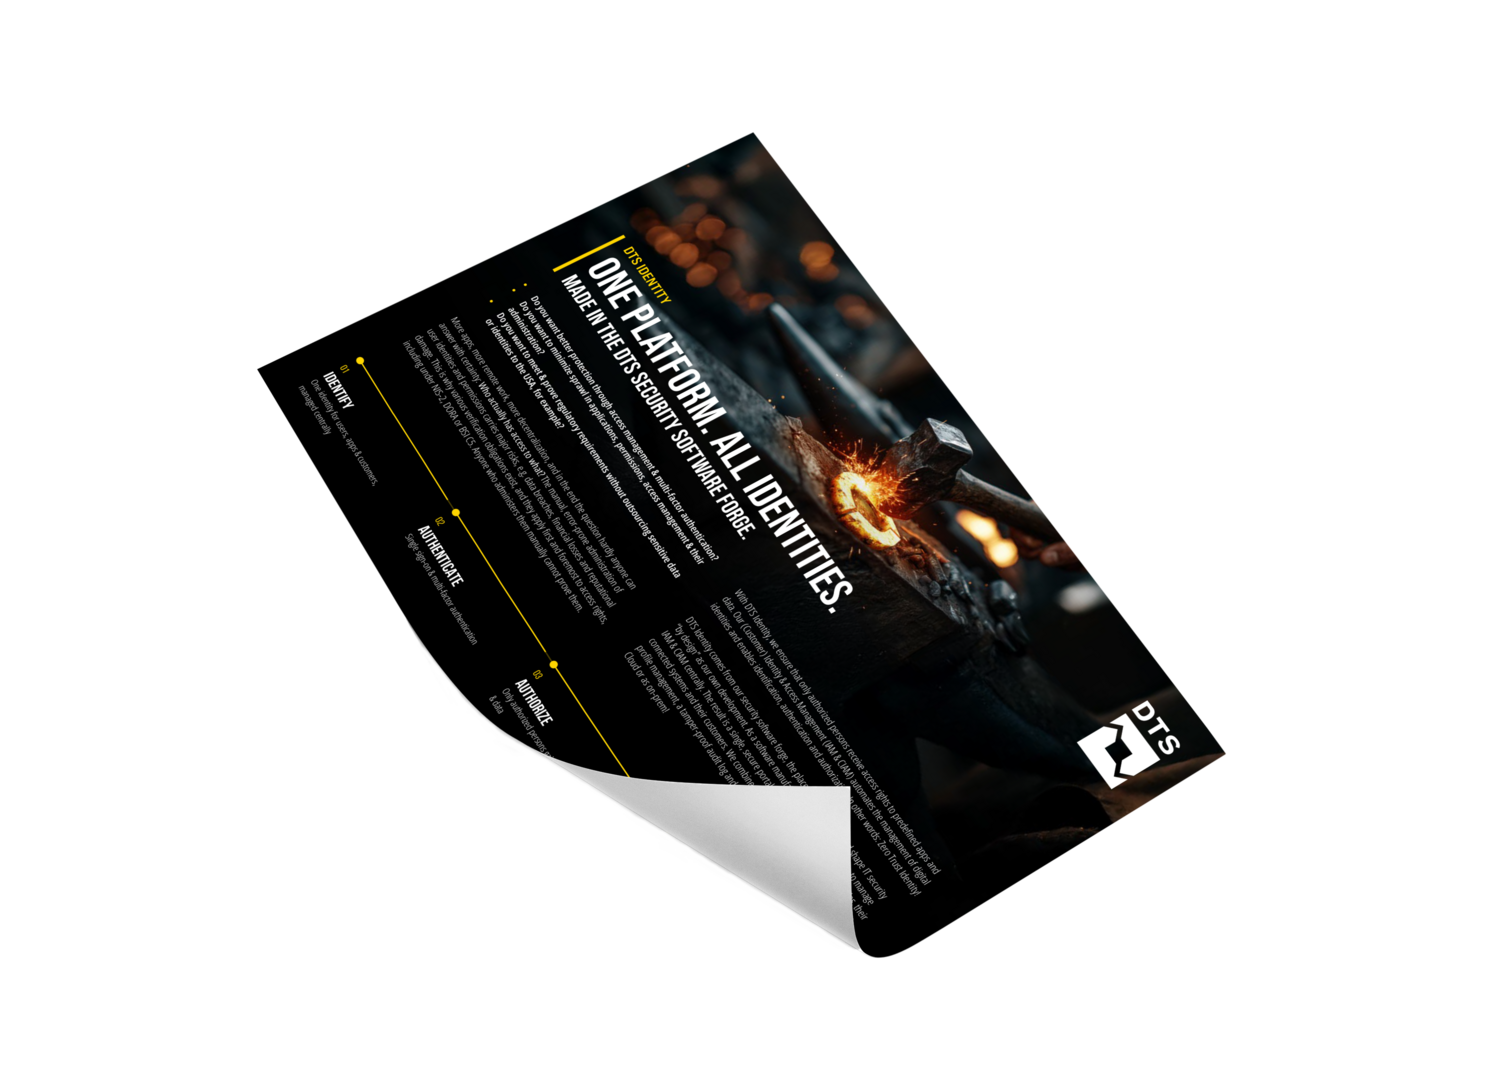
One platform.
All identities.
Forged in the DTS Security Software Forge
Do you want to protect yourself better with access management and multi-factor authentication?
Do you want to minimise sprawl in applications, permissions, access management and their administration?
Do you want to meet and prove legal requirements without outsourcing sensitive data or identities, e.g. to the USA?
More apps, more remote work, more decentralisation – and in the end, the question that hardly anyone can answer with certainty: Who actually has access to what? The manual, error-prone management of user identities and permissions entails major risks, e.g. data protection breaches, financial losses and reputational damage. This is why numerous verification obligations exist, and they apply first and foremost to access rights, e.g. under NIS-2, DORA or BSI C5. Anyone who only administers them manually cannot prove them.
With DTS Identity, we ensure that only authorised persons receive access rights to predefined apps and data. Our (Customer) Identity & Access Management (IAM & CIAM) automates the management of digital identities and enables identification, authentication and authorisation – in other words, Zero Trust Identity!
DTS Identity comes from our Security Software Forge – the place where we design and shape IT security as in-house development “by design”. As a software manufacturer, we have forged the platform to manage IAM & CIAM centrally. The result is a single, secure portal for users and apps – for entire companies, their connections and customers. We combine intuitive, SME-friendly access control, rights and profile management, a tamper-proof audit log and targeted alerts – scalable from the German, certified DTS Cloud or as on-prem!

The service
Our DTS Identity in detail:

1. Identify: One identity for users, apps and customers – centrally managed
2. Authenticate: Single sign-on and multi-factor authentication
3. Authorise: Only authorised persons gain access to apps and data
= Zero Trust Identity: IAM & CIAM from a single source
All apps. Secure login.
Companies have countless apps or microservices that are accessed by different user groups. There is a lack of overview and control. With DTS Identity, all apps can be bundled and are visible at a glance. Via single sign-on (SSO), every user can log in to their respective local or cloud apps through multi-factor authentication (MFA). This means that you or your customers log in centrally only once, see all the apps released for them and have direct access. The second factor also works without a smartphone, via hardware tokens, pre-registered security keys or temporary access codes – and can even be delegated to an existing privacyIDEA server. In addition, existing directories can be used for authentication, group management and attribute storage via an AD/LDAP connection.
Employees, customers, partners
DTS Identity can be provided for employees, customers and partners. The central identity management defines in just a few clicks for whom and for which apps the desired access policies apply, for B2B, B2C and B2E. This can also be coupled with provisioning/SCIM for each application at the “access level”. With the help of role-based access control (RBAC), it is also possible to assign different roles and predefined rights.
One dashboard. Everything in view.
The dashboard enables simple management. Every user can edit their data, settings and authentication factors in the self-service interface – incl. favourites and sorting in the application area. Admins see all activities in the platform dashboard, incl. attack detection and the actual MFA coverage of the entire user base. They can flexibly configure and enforce connected organisations, apps, APIs, users, permissions, roles and MFA – in 16 fully translated interface languages.
Less manual work, more core business
Manual work belongs in the forge – not in your user management. Manually managing user accounts and access rights as well as securing sensitive data is time-consuming and error-prone. We minimise this effort through automated rights management, access recertification, cross-site on- and offboardings as well as workflows that let you request or approve applications as needed. “On the side”, a concrete permission concept emerges – and compliance evidence is generated during ongoing operation. The integrated security health assessment continuously checks your own configuration against NIS-2, DORA or ISO 27001, among others, with a concrete gap list for each. Getting started is easy too: A guided assistant creates a suitable checklist that ticks itself off based on the current configuration.

CIAM – the customer experience counts!
The digital transformation is also changing the way you interact with your customers. Customer expectations of the user experience are high, especially when it comes to easy access combined with security. A CIAM is essential for the customer journey. DTS Identity can be embedded in customer applications and online services for customers. A transparent and secure user experience is guaranteed in every phase of the customer lifecycle. In acquisition and customer retention, it helps through simple registration via passwordless email login, SSO and fast onboarding. A registration policy defines who is allowed to self-register – any address, no disposable addresses or business addresses only. The check is performed against included domain lists, without any external service. This is a strong GDPR argument, as no additional processor comes into play. The catalogue comprises over 50 login connections, incl. European eIDs (German online ID card, DATEV). On top of that, the appearance editor provides completely individual branding of the login page, also with live preview. The platform supports your customer loyalty through dynamic extensibility of profiles for personalised customer experiences: Custom attributes are created from a toolkit of 30 pre-translated fields, and customers can transparently view and update their profiles as appropriate – all in compliance with all data protection regulations.
We see. We do. Safe!
Identity theft and fraud is one of the biggest cyber threats. Without an IAM & CIAM in particular, vulnerability is enormous, above all because compromised users usually have many accounts and access rights. As a security software manufacturer, preventing this is part of our self-image. On the one hand, by enforcing the least privilege principle. On the other hand, through numerous security features: Passwords for external systems are encrypted in the browser and are never viewed via DTS Identity. As protection against brute force attacks, the software compares common passwords with the user’s choice and prompts them to change it if necessary. If compromised login data is used, breached password detection identifies the user and the password and offers a direct response.
And the hammer never rests in our software forge: Every account now carries a risk score. This makes critical accounts visible at a glance. Attack detection shows the trend of repelled login attacks over the last 30 days, broken down by attack type and origin. Impossible travel automatically triggers a freely definable response, from a renewed factor check to logout across all apps. Access via public VPNs and open proxies is detected and can be controlled via access policy. And for emergencies, governance is firmly anchored: Break-glass emergency access based on the four-eyes principle is time-limited, without permanent rights and fully audited.
The next workpiece is already on the anvil: AI agents act autonomously with real access rights – every unsecured agent identity is a new gateway for attackers. That is why we will soon be bringing the protection of AI identities into DTS Identity.
Identify!
DTS Identity is exactly one platform for all identities and enables IAM & CIAM at the highest level. It ensures that only authorised and entitled identities access IT resources. It enables simple authentication and central profile and rights management. It protects sensitive data, increases your security level and forms the basis for meeting compliance requirements and internal policies. It increases productivity and efficiency. It offers a great user experience and relieves you and your IT team. We provide DTS Identity with all features from our DTS Cloud or as on-prem, incl. support – Easy to Use & Easy to Pay!
See also:
DTS Identity Client: With the DTS Identity Client, we harden the solution even further and enable additional Zero Trust Identity down to the level of the end device. Take a look at our DTS Identity Client one-pager!
NIS-2: Want to implement NIS2 requirements successfully and sustainably? Take a look at our additional flyer on DTS Identity & NIS2!
Secure remote access: Only 14 % of all users use VPNs to secure their identity, even though this contributes significantly to protection. Take a look at our additional flyer on secure remote access with DTS Identity!
Coming soon – AI identities: Machine identities already outnumber human ones many times over – and “agentic AI” is scaling this further. That is why we are also forging the protection of AI identities in DTS Identity: Managing, authenticating and limiting AI agents in one IAM.
ASK IT: FAQ around the topic "DTS Identity"
DTS Identity is a centralized platform for Identity & Access Management (IAM) and Customer Identity & Access Management (CIAM). It decouples identity and access management from individual applications and consolidates it into a single platform. Organizations can centrally manage all identities—including employees, customers, partners, and machines (B2E, B2B, B2C, and M2M)—and define who is allowed to access which applications and data, from which devices. DTS Identity is hosted in the certified DTS Cloud in Germany.
DTS Identity supports the integration of any application that uses the OpenID Connect (OIDC) or SAML authentication standards, including both on-premises applications and cloud-based services. With Single Sign-On (SSO), users authenticate once and are then presented with all applications they are authorized to access. Existing directory services can continue to be used through Active Directory (AD) or LDAP integration for authentication, group management, and attribute storage.
Yes. DTS Identity supports Multi-Factor Authentication (MFA), including passwordless authentication, and is fully FIDO2-compliant. Users can manage their authentication methods through a self-service portal, where they can also update their profile information and personal settings.
DTS Identity combines two key access control mechanisms. Conditional Access grants or denies access based on predefined conditions such as location, user role, device, or time of day. Role-Based Access Control (RBAC) automatically assigns permissions according to a user's designated role. The platform follows the Principle of Least Privilege, ensuring that every identity receives only the permissions required to perform its tasks.
The DTS Identity Client extends identity verification to include the security posture of the endpoint device. It evaluates factors such as device health, permissions, and compliance status before granting access. This closes a common gap in traditional IAM solutions, as desktops and laptops are associated with more security incidents than any other device type—especially when protected by passwords alone. By incorporating device trust into the authentication process, DTS Identity enables a robust Zero Trust Identity approach.
DTS Identity is delivered from the DTS Cloud in Germany, providing certified infrastructure and 24/7 support. This enables organizations to meet regulatory and compliance requirements without transferring sensitive identity data to the United States. Identity information is stored in a dedicated database.
Identity & Access Management (IAM) governs access for internal identities, including employees, contractors, and systems. It focuses on authorization models, role management, governance, and auditability.
Customer Identity & Access Management (CIAM) is designed for external users such as customers and business partners. In addition to security, it emphasizes user experience by providing seamless registration, fast onboarding, and a unified customer profile.
DTS Identity combines both IAM and CIAM capabilities within a single platform, eliminating the need to operate separate identity management systems.

Let's have a talk!
Get free and easy advice.